Cofense Triage
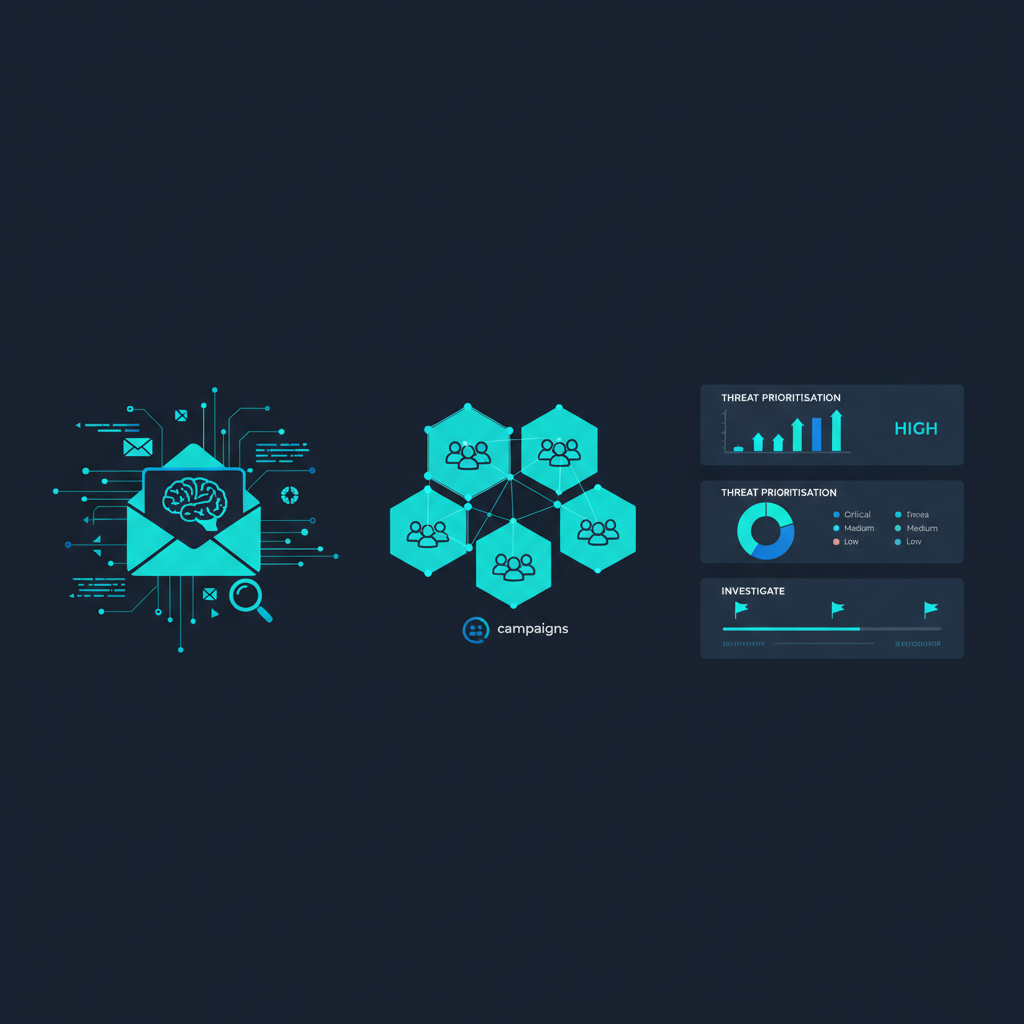
Cofense Triage uses AI-powered threat triage to automate analysis, cluster related threats into campaigns and prioritise confirmed phishing threats, enabling SOC teams to investigate faster, reduce analyst workload and strengthen phishing response across SEG and Microsoft 365 environments.
Why Phishing Triage Matters
As phishing reporting rates improve, security teams face a growing challenge. The volume of reported emails requiring investigation can quickly overwhelm manual analysis processes.
Without automated threat triage, analysts spend significant time reviewing false positives and low-priority reports. This diverts attention from genuine, high-severity phishing threats that demand immediate action.
Cofense Triage uses AI-powered threat triage to automate analysis, cluster related threats into campaigns and prioritise every reported email. Security teams handle higher reporting volumes without adding analyst headcount and respond to confirmed threats faster, complementing existing SEG and Microsoft 365 security controls.
Scale triage without expanding analyst headcount
Automate analysis of every user-reported email
Cluster related phishing emails for faster investigation
Prioritise confirmed threats by severity and scope
Focus analyst effort where it delivers the greatest impact
Cofense Triage Capabilities
From detection to response, designed to handle the volume and complexity of real-world phishing investigation workflows.
AI-Powered Threat Triage
Automated threat triage analyses every user-reported email using AI-powered analysis, separating genuine threats from false positives without manual review.
Campaign Clustering
Cluster related threats from multiple reporters into single campaigns, enabling security teams to investigate and remove whole campaigns, not just individual emails.
Threat Prioritisation
Prioritise phishing threats by severity automatically, directing analyst resources to the most critical incidents first.
Faster Incident Response
Respond to confirmed threats significantly faster than manual triage processes allow, reducing exposure and dwell time.
Reduced Analyst Workload
Eliminate the manual burden of investigating every reported email, freeing analysts to focus on confirmed, high-priority threats.
SOC Integration
Integrate with SIEM platforms, SOAR workflows and ticketing systems to connect phishing triage into broader incident response.
Related Cofense Technologies
Cofense Triage sits at the centre of the phishing detection and response workflow. Employees report suspicious emails via one-click Outlook reporting, Triage uses AI-powered threat triage to analyse and cluster threats into campaigns, and Cofense Vision enables threat autoquarantine and one-click threat removal across all affected inboxes.
Cofense Triage FAQs
Download the Official Cofense Datasheets
Enter your work email to access the official Cofense datasheets for Triage, Vision and integrations.
Relevant Cofense Datasheets
2 datasheets available
Cofense Triage & Vision Integrations
How Cofense Triage and Vision integrate with SIEM, SOAR, analysis and threat intelligence platforms for enterprise phishing operations.
Cofense Phishing Detection & Response (PDR)
How Cofense PDR identifies and remediates advanced phishing threats that bypass traditional perimeter defences.
Enter your details to download all datasheets
Request a Cofense Triage Demo
Reduce investigation time, improve analyst efficiency and accelerate phishing response across your Microsoft 365 environment. Tell us about your SOC workflows and we'll recommend the right approach.