Cofense vs Abnormal AI for Enterprise Phishing Detection & Response
Compare Cofense vs Abnormal AI to understand the differences between AI-driven email security and phishing detection and response designed to help security teams investigate, respond to and reduce phishing risk.
Understanding the Different Security Approaches
Both Cofense and Abnormal AI help organisations reduce phishing risk, but they focus on different parts of the phishing defence lifecycle.
Phishing attacks have evolved beyond traditional spam campaigns. Modern attackers use AI-generated content, compromised accounts, business email compromise (BEC) and sophisticated social engineering techniques that can bypass preventative email controls.
Understanding the different approaches helps enterprise buyers evaluate which platform aligns with their security strategy, existing technology stack and operational maturity. Modern defence spans detection, user reporting, threat investigations, campaign visibility, rapid remediation and human risk reduction.
Where Each Platform Excels
Both platforms bring distinct strengths to enterprise phishing defence programmes.
Abnormal AI is recognised for:
- Behavioural AI detection
- Cloud-native email security
- Identity-based analysis
- Business email compromise detection
- Account takeover prevention
- Automated pre-delivery detection
Cofense is recognised for:
- One-click employee reporting
- Phishing investigation workflows
- Campaign detection and intelligence
- Inbox remediation
- Human risk management
- Operational phishing response maturity
Many enterprise organisations deploy both approaches as complementary layers rather than choosing between them.
Detection Philosophy
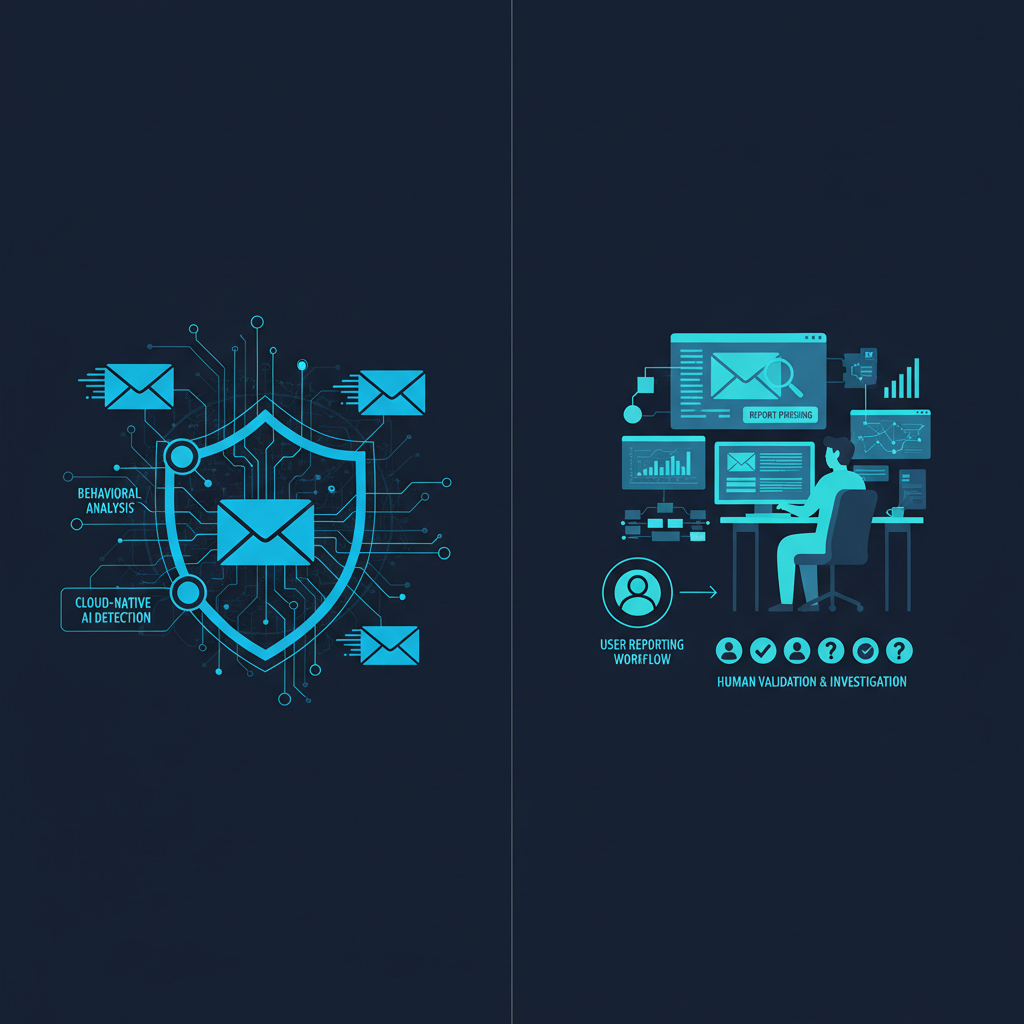
One of the biggest differences between the platforms is how phishing attacks are discovered.
Abnormal AI
Emphasises behavioural AI, machine learning, identity signals, automated detection and cloud-native analysis to prevent threats before delivery.
Cofense
Combines employee reporting with phishing-specific AI, human validation, campaign intelligence and analyst workflows designed for post-delivery investigation.
For many organisations, user reporting remains an important source of phishing intelligence because employees often identify suspicious emails that require investigation, even when automated detection technologies are in place.
Investigation & Response
Modern phishing defence is no longer solely about stopping malicious emails before they reach users.
Abnormal AI supports:
- Automated detection workflows
- Identity-based investigation
- Cloud-native response
- Pre-delivery threat blocking
- Behavioural anomaly alerts
Cofense supports:
- Rapid phishing reporting
- Threat investigations
- Campaign correlation
- Inbox remediation
- Operational visibility
- Security team workflows
- SOC, SOAR and SIEM integration
While AI-driven prevention can reduce the number of malicious emails reaching users, post-delivery detection and response helps organisations investigate suspicious emails, understand attack scope and respond quickly when threats bypass preventative controls.
Human Risk & Employee Reporting
Technology alone cannot eliminate phishing risk. Modern defence also depends on employees recognising and reporting suspicious messages quickly.
Cofense supports this through one-click phishing reporting, phishing defence training, phishing simulations and human risk management, creating a continuous feedback loop where employee reporting contributes to faster investigations, improved campaign intelligence and stronger organisational resilience.
The feedback loop
Employee reporting feeds directly into investigations, campaign intelligence and remediation, creating faster response, stronger resilience and reduced human risk over time. This continuous cycle strengthens operational defence maturity across the organisation.
Enterprise Operations
Both platforms are designed for enterprise deployment, with different operational considerations for security teams.
Abnormal AI enterprise capabilities:
- Cloud-native deployment
- Microsoft 365 integration
- Google Workspace security
- API-driven architecture
- Automated detection at scale
- Identity and Zero Trust alignment
Cofense enterprise capabilities:
- SOC-aligned workflows
- SIEM and SOAR integration
- Microsoft 365 phishing response
- Enterprise deployment scalability
- IOC and DMARC-aligned processes
- Operational response maturity
Enterprise organisations often evaluate how each platform integrates with existing security operations, SIEM and SOAR investments, and Microsoft or Google Workspace environments.
Which Organisations Typically Choose Each Platform?
The right platform depends on organisational priorities, existing technology and operational maturity.
Abnormal AI is commonly selected by organisations that prioritise:
- Behavioural AI detection
- Automated pre-delivery prevention
- Identity analysis
- Cloud-native protection
- Business email compromise detection
- Zero Trust-aligned email security
Cofense is often selected by organisations looking for:
- Employee reporting workflows
- Phishing investigations
- Campaign visibility and intelligence
- Inbox remediation
- Human risk management
- Operational phishing response
- SOC, SOAR and SIEM-aligned defence
Many enterprise organisations deploy multiple layers of protection, combining AI-driven preventative email security with post-delivery phishing detection and response capabilities to improve resilience against modern attacks.
Cofense vs Abnormal AI FAQs
Compare Cofense and Abnormal AI
The right phishing defence strategy depends on your security objectives, existing investments and operational maturity. Speak with Wise Fish to evaluate how Cofense can complement your AI-driven email security, strengthening detection, investigations, employee reporting and response capabilities.
Compare Phishing Detection and Response Platforms
Tell us about your phishing defence requirements and we'll help you evaluate the right approach for your organisation.